


Satoshi’s wallet: a prime target for quantum attacks
Satoshi’s original Bitcoin wallet, which contained 1.1 million BTC, is being viewed by researchers as a quantum vulnerability. They are assessing how the increasing computing power of computers could impact early Bitcoin addresses.
Satoshi Nakamoto is estimated to have 1.1 Million Bitcoins (BTCIt is sometimes described as “the ultimate crypto currency” “lost treasure.” The digital ghostship has never seen a transaction on blockchain since its inception. It has now become legend that this massive collection, valued at between $67 and $124 billion, is still there.
For a growing group of physicists and cryptographers, the threat is also seen as one that could cost billions. It isn’t a hacker or server breach, it’s the rise of a new computing form. quantum computing.
Quantum machines, as they move from the theoretical labs of research to working prototypes that are powerful enough to be used in real-world applications, pose a threat to cryptographic systems. The encryption used to protect Satoshi’s coins as well as the Bitcoin network, and other parts of global financial infrastructure are all included.
This is not an afaraway “what if.” Race to develop both quantum computers and an quantum-resistant defense It is one the most crucial and best-funded technologies of our time. This is the information you need.
Satoshi’s wallets from the early days are easy targets for quantum attacks
Modern Bitcoin wallets usually hide the public keys until there is a transaction. Satoshi’s pay-to public-key (P2PK), legacy addresses, do not. Their public keys remain permanently visible on chain.
In order to fully understand the danger, you must first recognize that Bitcoin addresses are not created equally. Satoshi’s addresses from 2009 and 2010 are the source of vulnerability.
Most Bitcoin today is held in pay-to-public-key-hash (P2PKH) addresses, which start with “1,” SegWit addresses that begin with “bc1.” The blockchain stores only the hash when coins arrive at these types of addresses. It only shows the real public key after the coins have been spent.
Consider it similar to a deposit box at the bank. The mail slot is a hash of the address; anyone who can see it may drop in money. The metal lock behind the slot contains the public key. Lock and mechanism are hidden from view. The public key is the “lock”The private key will only be revealed when you choose to spend the coins. “unlocks” it.
Satoshis coins are, however, stored in older P2PK address. This legacy format does not have a hash. In our analogy, we can see that the public key, or the lock, is permanently and visibly recorded on the Blockchain.
This does not affect a classic computer. Even though it is practically impossible to reverse engineer a public-key to get the private key, this still remains a possibility. A quantum computer can use the public key as a detailed plan. The lock is open to anyone who wants it.
Shor’s algorithm breaks Bitcoin with quantum machines
Elliptic Curve Digital Signature Algorithm, the security algorithm for Bitcoin (ECDSA), is based on mathematics that are computationally impossible to reverse by classical computers. Shor’s algorithms, when run by a powerful enough quantum computer, are designed to reverse that math.
Bitcoin’s security model ECDSA is the foundation of a scalable system. The strength of the system comes from its one-way assumption. A private key can be multiplied by one point of a curve in order to obtain a public-key, but its reverse is impossible. The Elliptic Curve Discrete Logarithm Problem is the name of this problem.
The classical computer is not able to perform any of these functions. “divide” This operation. This operation’s only choice is brute-force, which involves guessing each possible key. There are 2256 possible keys, which is a huge number that exceeds even the known number of atoms. Bitcoin will remain safe against all supercomputers, both classical and future.
It would calculate. The quantum computer would be able to calculate.
Shor’s Algorithm, developed in 1994, is the tool to do this. The algorithm is a theoretical process developed in 1994. powerful quantum computerThe algorithm is able to use quantum superpositions in order find hidden patterns of mathematics, namely the period. The algorithm can reverse engineer a public key in hours or even days to determine the private key behind it.
The attacker does not need to hack into a computer. The attacker could harvest all the P2PK keys that were exposed on the blockchain and feed them to a quantum computer, then wait until the private keys are returned. They could then sign the transaction to move Satoshi’s 1.1 millions coins.
Did You Know? According to estimates, a computer with over ten million transistors would be required to break the encryption of Bitcoin. 2,330 stable logical qubits. Due to the noise and errors that are present in current qubits, it is believed by experts that a fault-tolerant device would require more than one million physical qubits.
Are we close to Q-Day yet?
Companies like Rigetti, Quantinuum and others are racing against the clock to create a quantum computer that is cryptographically useful. The timeline has shrunk from decades to just a few years.
“Q-Day” This is the hypothetical time when a quantum computing system can break current encryption. It was thought to be a long-distance possibility for many years. “10-20-year” Problem, the timeline has now become increasingly compressed.
Quantum error-correction is why 1,000,000 physical qubits are needed to produce 2,330 logical qubits. The qubits themselves are fragile. Qubits are fragile and noisy. They can be affected by even small vibrations or temperature fluctuations, and radiation. This could cause them to lose their quantum state and result in errors.
For a calculation that is as complicated as breaking ECDSA you will need stable logical quabits. For a single qubit of logical information, it may be necessary to combine hundreds or thousands of physical qubits. The system overhead is required to maintain stability.
The quantum race is accelerating rapidly.
-
Quantinuum Rigetti IonQ and other tech giants, such as Google, IBM and Microsoft, have publicly announced aggressive quantum roadmaps.
-
Rigetti is on course to achieve a system with 1,000 or more qubits by 2027.
-
These publicized achievements do not include classified research at the state level. First nation to achieve Q-Day would theoretically have the key to all global intelligence and financial data.
Prior to an attack, the defense must therefore be constructed and ready for deployment.
The quantum attack on Bitcoin exposes millions of bitcoins
According to a report by the 2025 Human Rights Foundation, 6.51 Million BTC are in addresses that could be vulnerable, and 1.72million of them, including Satoshi, is considered unmovable.
Satoshi’s wallet, although the largest prize is not only that. A date in October 2025 report Human Rights Foundation has analyzed all of the blockchain to determine its quantum vulnerabilities.
Findings were shocking
-
Quantum attacks with a long range are capable of compromising 6.51 BTC.
-
The estimated Satoshi BTC of 1.1m BTC is among the 1.72m BTC that may be in dormant addresses or lost.
-
A further 4,49 million BTC are vulnerable, but can be protected by migration. This suggests that their owners may still have the ability to act.
Users made the critical error of reusing addresses. This 4,49,000,000 BTC is theirs. The users used P2PKH modern addresses but, after they spent (which revealed their public key), received money back at the same address. It was not uncommon in the early 2010. Reusing the same address permanently exposes their public key, making their modern wallet just as vulnerable to attack as Satoshi.
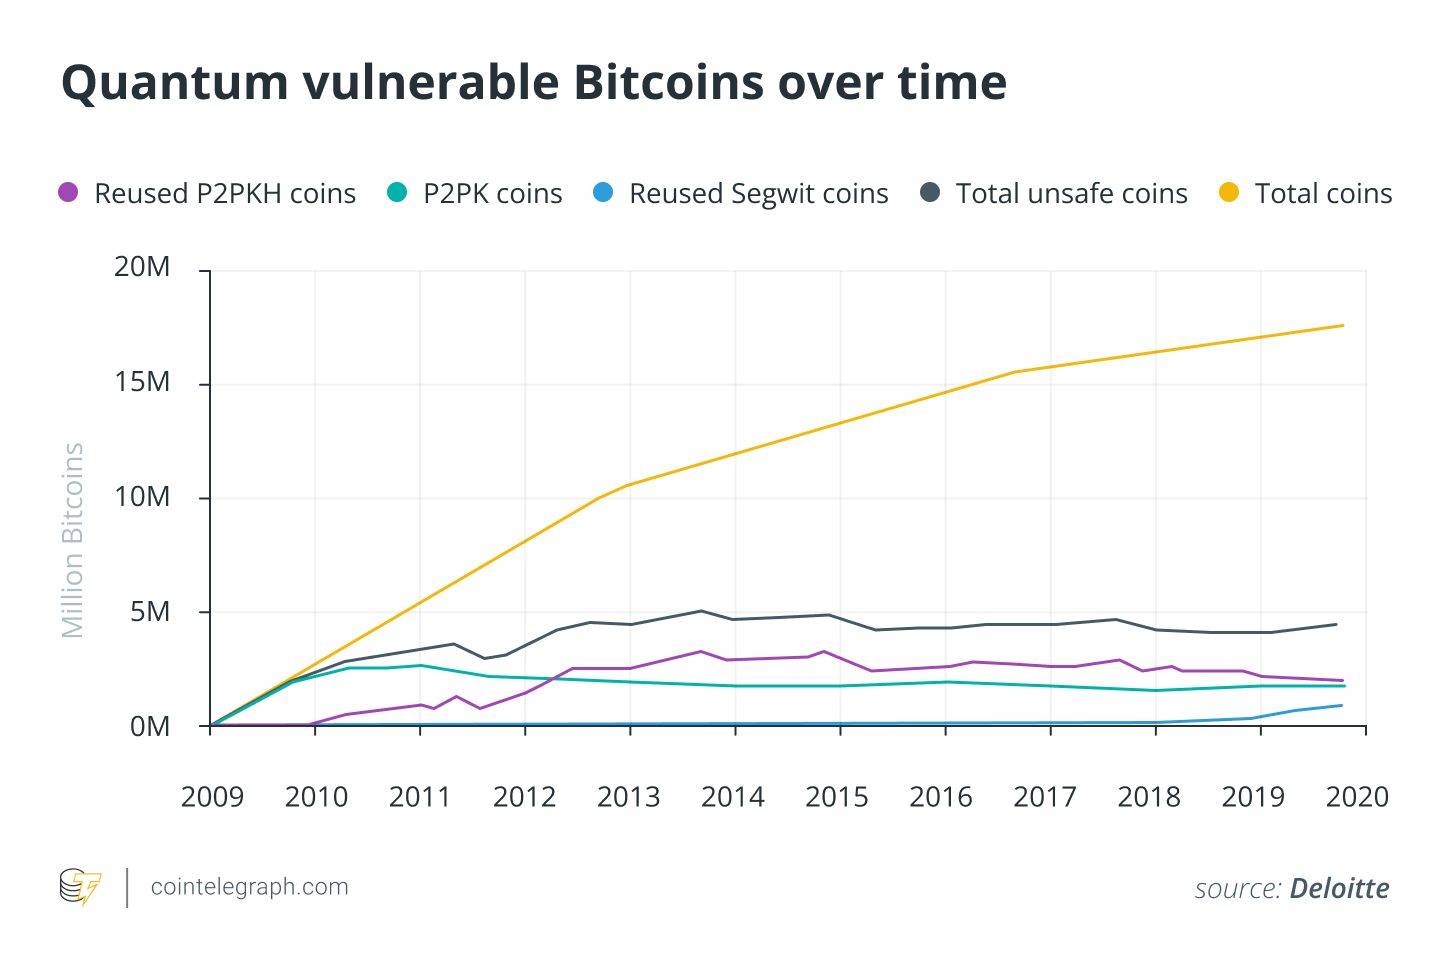
The simple act of moving Satoshi’s coins as proof that an attack was successful would be the case if a hostile actor reached Q-Day first. The act of moving Satoshi’s coins would serve as proof that the fundamental security of Bitcoin had been compromised. It could cause a market panic and even a run on exchanges.
Did You Know? The most common tactics used by terrorists are: discussed You can learn more about it here. “harvest now, decrypt later.” Using quantum computers, malicious actors have already begun recording data that is encrypted, including internet traffic, blockchain public keys and bitcoin addresses.
Bitcoin quantum safe protection: How to switch?
It is now a global movement to adopt new, quantum-resistant technology. This would mean a network upgrade or fork to the new algorithm.
The cryptographic community does not wait for it to happen. Solution is post-quantum cryptography (PQC)A new generation of cryptographic algorithms based on more complicated mathematical problems, which are thought to provide security against quantum and classical computers.
Many PQC algorithms use structures like lattice-based encryption instead of elliptic curvatures. Leading this initiative is the US National Institute of Standards and Technology.
-
The National Institute of Standards and Technology will publish the finalized PQC standard in August 2024.
-
The key one for this discussion is ML-DSA (Module-Lattice-based Digital Signature Algorithm), part of the CRYSTALS-Dilithium standard.
-
OpenSSH 10.0 is being adopted by the wider tech industry. OpenSSH 10.0 will be available by the end of 2025. made Cloudflare made the PQC algorithm default. Cloudflare also reported that most of its website traffic was now PQC protected.
Bitcoin’s path forward is almost certain to be implemented through a soft-fork, a system update that would affect the entire network. This update would introduce new address types that are quantum resistant, including the recently proposed “P2PQC” addresses. This would not require anyone to relocate. The users would be able to send funds involuntarily from the older addresses that are vulnerable, such as P2PKH, SegWit or P2PKH, into these new and secure addresses. The SegWit update was implemented in a similar way.
“This article is not financial advice.”
“Always do your own research before making any type of investment.”
“ItsDailyCrypto is not responsible for any activities you perform outside ItsDailyCrypto.”
Source: cointelegraph.com


