


Aztec Network’s Router Contract is the topic of news following a suspicious Ethereum transaction. [ETH] blockchain. The loss was estimated at $2.19million.
It is not the address that matters, but rather what you put in your wallet. “0x0f18….edd17” The transaction was funded by money taken from the Protocol’s Router Contract.
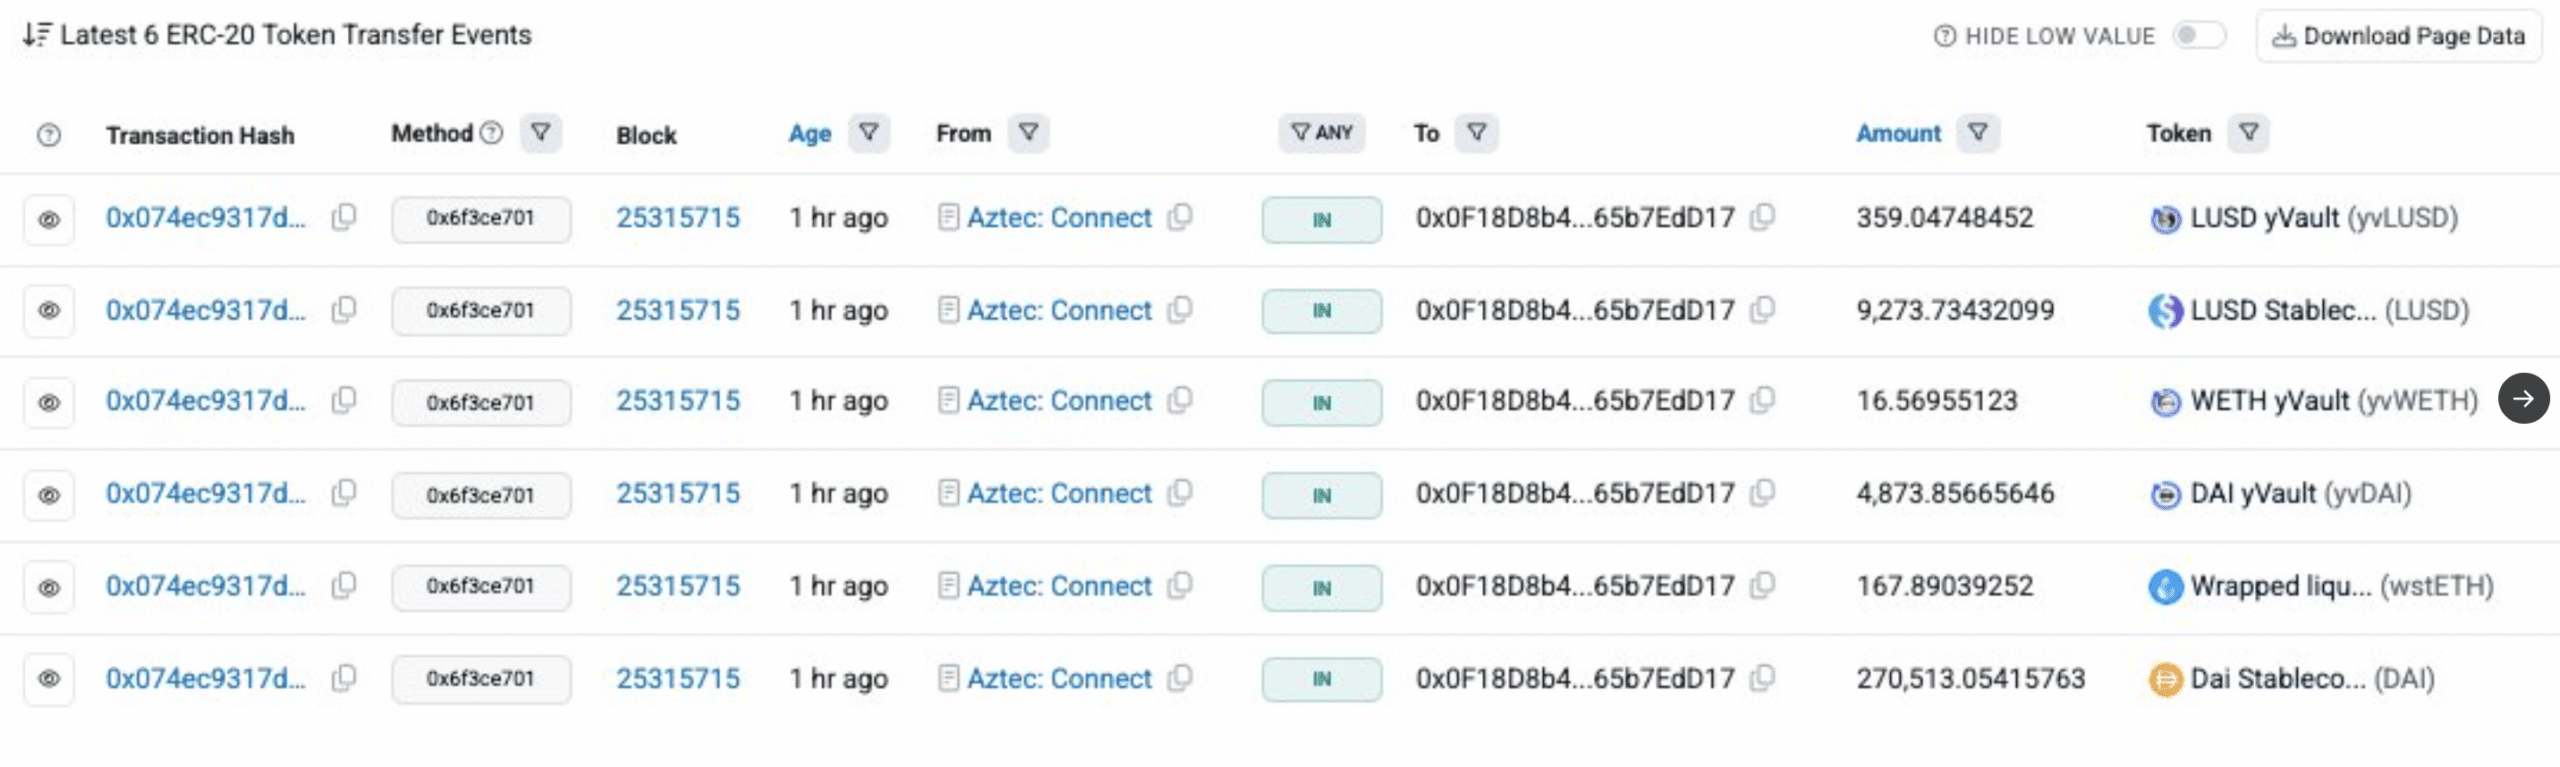
According to CertiKThe attack was “suspicious” The attacker may have exploited an insecurity of the smart contract by gaining unauthorized entry to the protocol funds or altering the logic to steal assets.
A possible smart contract validation flaw
There were some clues that suggested the handling of the proof data by the protocol may have been flawed. smart contract validation process. It seemed that the problem was with the specific function. CalculateRootHashes()The…………… c…………… _proofData But only the first half of it was examined.
The middle section of the same _proofData Payload is the information that contains data. processDepositsAndWithdrawals() Afterwards, tokens are used to make transfers.
A malicious proof could be created by an attacker in which the unverified middle portion contained fake instructions on how to deposit or withdraw money, while the verification section remained valid, and the security check of the protocol was passed.
The contract, on its side, ended up executing unauthorized token transfers because the instructions were not properly authenticated prior to processing. There appeared to be an apparent discrepancy in what was confirmed and what was executed.
Other incidents of this nature
Raydium has also been found to be a. coding error The old AMM program, which was used by the company before AMM V3, caused some $1.34,000,000 worth of crypto to be taken from 5 pools.
Here’s another governance takeover attack An exploiter stole about $1.5 Million in Ethereum From a balancer liquid pool.
Recently, a new attack that targets Ethereum’s Alephium tokenBridge has also been discovered. This exploit targets Ethereum’s Alephium TokenBridge. $815,000 was drained In seven minutes, using three out of four compromised keys used to sign forged VAAs.
A Quantstamp independent investigation found the same thing. Humanity Protocol linked a targeted phishing attack The attacker acquired administrative credentials and upgraded contracts. He also transferred Ethereum tokens.
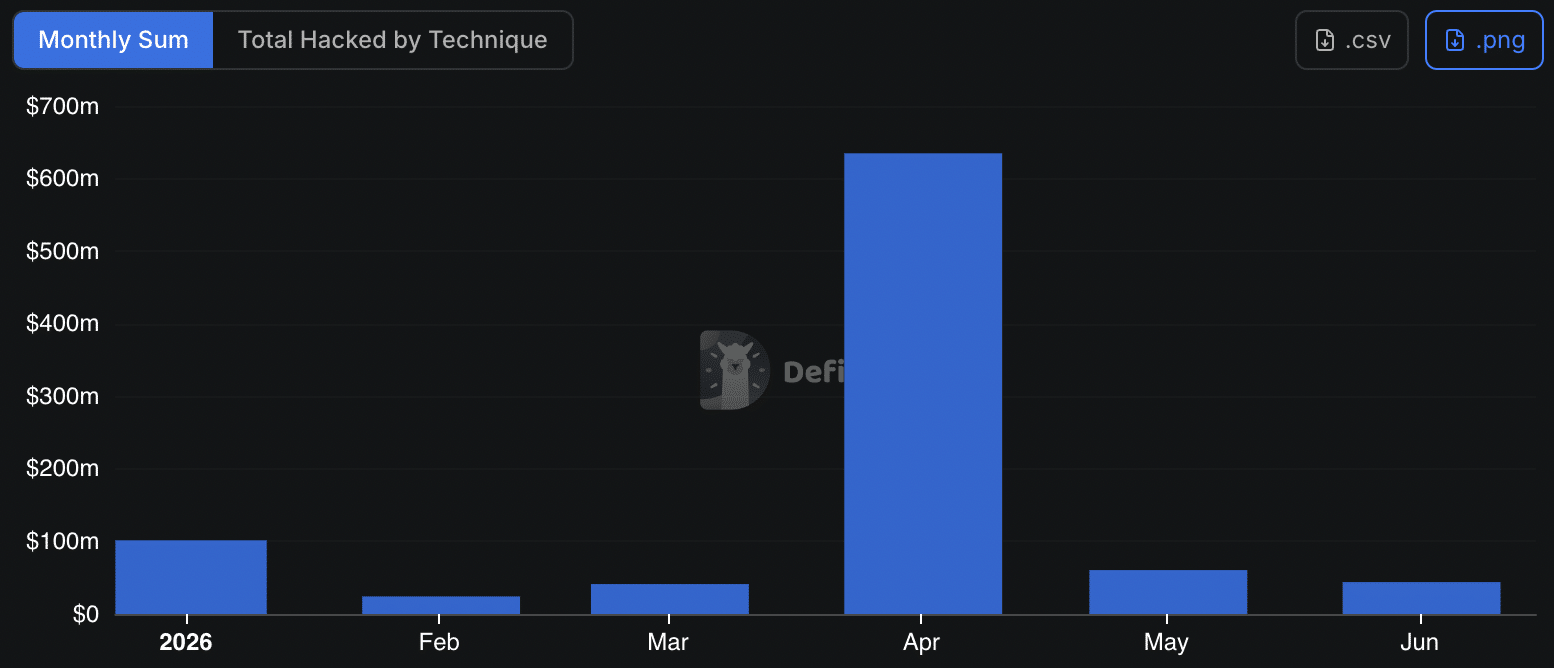
DeFiLlama’s data shows that the total value of hacking (USD), as a whole, has reached $81.73 in only 30 days. The highest amount of money has been lost so far in April, with $634.85 millions.
Final Summary
- It appears that _proofData did not perform a complete verification.
- It is not the first time that DeFi has had security issues.
“This article is not financial advice.”
“Always do your own research before making any type of investment.”
“ItsDailyCrypto is not responsible for any activities you perform outside ItsDailyCrypto.”
Source: ambcrypto.com


